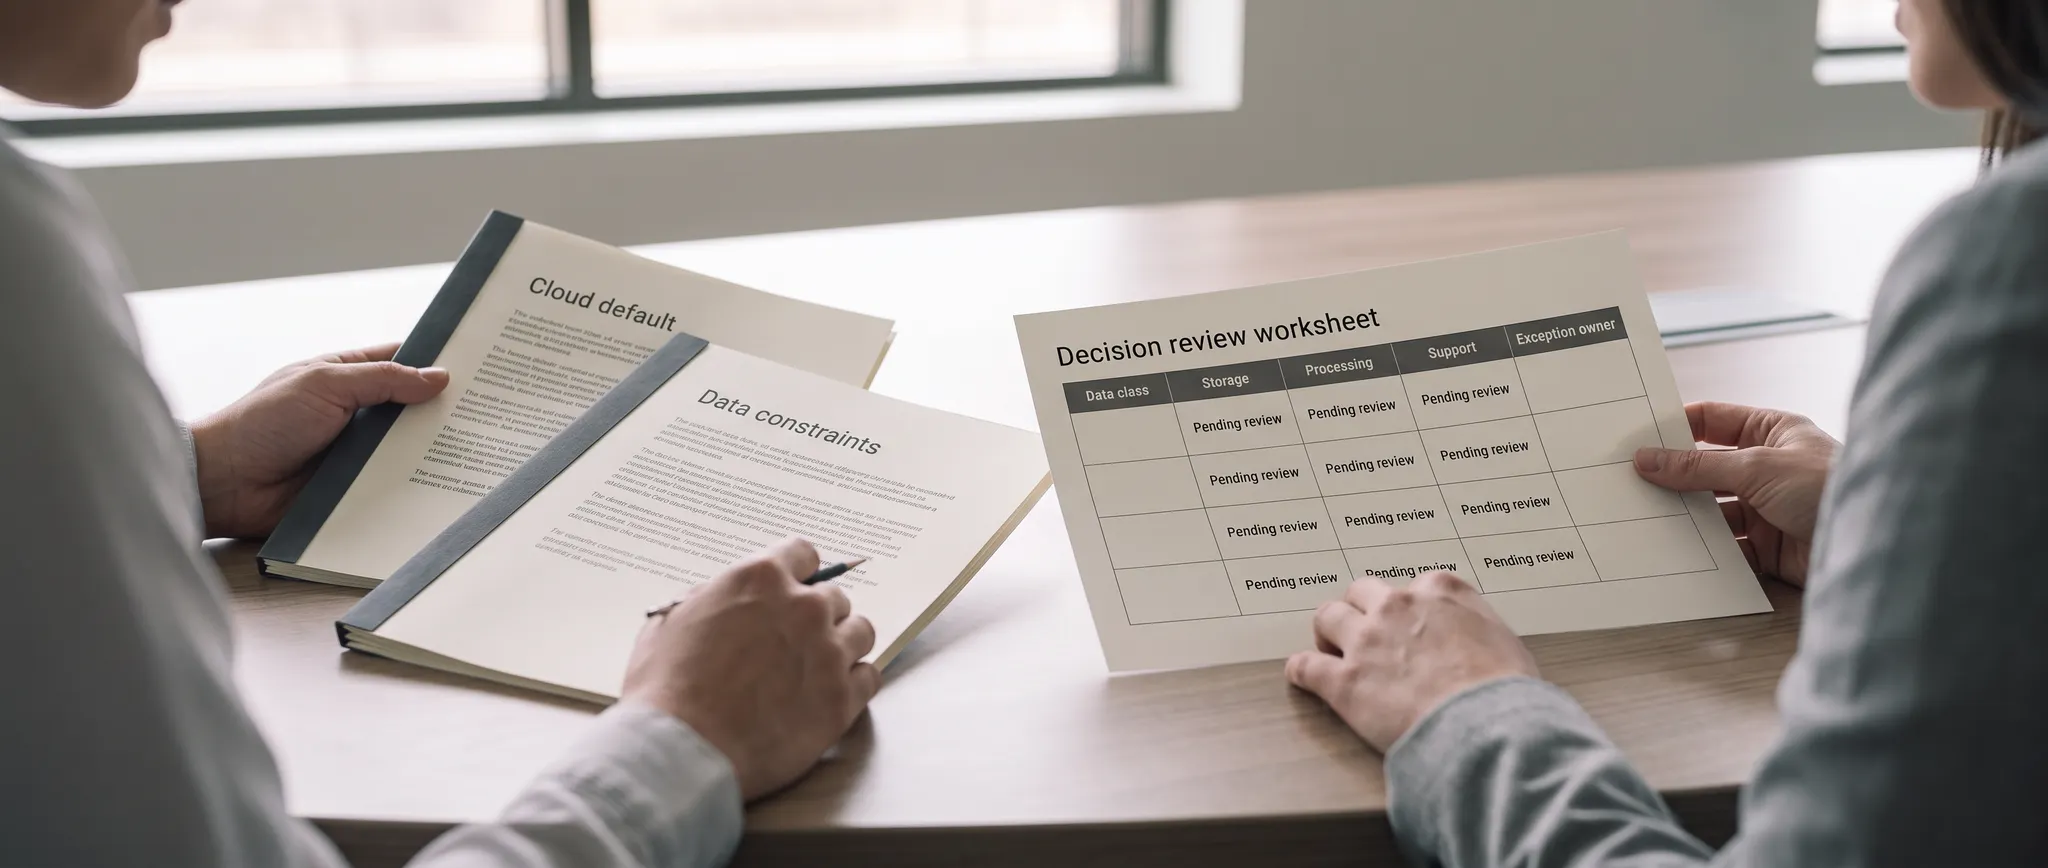
Somewhere in most large organizations around this period, two policies were written by two different departments and never read side by side. The first came from IT: new systems should be cloud by default, with on-premise deployment requiring justification. The second came from legal or compliance: certain categories of data must remain within specified borders, and cross-border transfer requires an approved mechanism. Both were sensible. Together they were a contradiction that surfaced, reliably, about six weeks into a procurement.
Where the Collision Actually Happens
The conflict rarely appears in strategy documents. It appears in a project. A business unit selects a system that solves a real problem. The economics are compelling, implementation is quick, and the cloud-first policy supports it. Then someone asks where the data will be stored, and the answer is a region that does not satisfy the residency requirement. The provider has no regional presence. The project stops, and the choices are all bad: abandon a good system, seek an exception that undermines the policy, or spend twelve months on an alternative that nobody wants. The default outcome, in practice, is the exception. Enough exceptions and the residency policy becomes a document that describes an aspiration rather than a control — which is worse than not having one, because it creates a false record of compliance.
Why Each Policy Was Written That Way
The cloud-first mandate was a response to genuine problems: aging hardware, deferred upgrades, unpredictable capital expenditure, and internal infrastructure that consistently underperformed what a specialist provider could deliver. Making cloud the default rather than an option was a deliberate lever to overcome institutional inertia. The residency rule was equally grounded. Regulated sectors face explicit requirements — in the GCC, financial services, healthcare and government-related data all carry location obligations, and similar rules exist across Europe, India, Russia and China. Cross-border transfer law adds a second layer, and enforcement in this area has become materially more aggressive since the transatlantic adequacy arrangements were struck down. Neither policy is wrong. The failure is that they were drafted independently, at different levels of specificity, by teams with different mandates, and never reconciled into a single decision rule.
What a Reconciled Policy Looks Like
The resolution is not to abandon either position. It is to make the residency requirement data-specific rather than blanket, and to make the cloud mandate conditional rather than absolute. Classify first. Most organizational data has no residency obligation at all. Marketing content, internal documentation, product information and much operational data can go anywhere. A smaller set — personal data of residents, regulated financial records, health information, government-related material — carries real constraints. A blanket rule applied to everything either over-restricts the majority or under-protects the minority. Write the rule by class, not by system. "Customer personal data for UAE-regulated entities must be stored in an approved in-country region" is enforceable. "Sensitive data must stay local" is not, because nobody agrees on what is sensitive. Make region availability a screening criterion. If a class of data has a residency requirement, provider region availability belongs in the initial vendor shortlist, not in the contract review after the business has fallen in love with the product. Distinguish residency from jurisdiction explicitly. Data stored in-country under a foreign-headquartered provider may still be reachable by foreign legal process. If the concern is legal access rather than physical location, an in-country region does not resolve it, and the policy should say so rather than implying it does. Define the exception process properly. Who can grant one, on what evidence, with what compensating controls, for how long, and with what review. Exceptions granted verbally and never revisited are how policy erodes.
Classify the data
Determine the specific obligations and applicable scope
Write a usable decision rule
Agree the class, deployment conditions and accountable owners
Screen the service
Check the exact edition and region before selection
Separate location surfaces
Review storage, processing, support and secondary copies
Govern exceptions
Specify evidence, authority, controls, expiry and review
Re-verify the arrangement
Track actual locations and material provider changes
Qualitative summary of this article's source text, not a measured outcome or performance estimate.
Practical Steps for Aligning the Two
- Build a single decision matrix. Data class down one axis, deployment options across the other, with the permitted answer in each cell. One page, agreed by IT, legal and the business, used at the start of every procurement.
- Audit the exceptions already granted. Most organizations have more than they think, some for systems that have since changed scope. This is usually the fastest way to find real exposure.
- Separate storage, processing, backup and support location. Policies typically address storage only. Backups in another region and support access from a third country are the most common gaps.
- Involve legal before the shortlist, not after. The cost of a residency problem discovered at contract stage is an abandoned evaluation. Discovered at requirements stage, it is a filter.
- Track provider region roadmaps. A provider that cannot meet your requirement today may be able to in twelve months. That changes the calculus on interim arrangements.
- Assume architecture will be hybrid. Some workloads local, some regional, some global. A policy that assumes a single answer will be violated by reality.
- Re-verify annually. Providers migrate services between regions, change sub-processors and add support locations. Compliance verified once is compliance assumed thereafter.
- Keep a register of where each regulated data class actually sits. Not where policy says it should be — where it is. The difference between those two documents is your risk position.
The AI Version of the Same Argument
The collision has recurred with AI services, in a sharper form. The organizational appetite is high, the productivity case is visible, and adoption is happening at the level of individual employees rather than procurement committees. Meanwhile the residency questions are harder to answer than they were for storage. Inference may run in a different region from the account. Prompt data may be retained for abuse monitoring in a location stated in documentation that changes. Sub-processors are numerous and sometimes undisclosed. Fine-tuning arrangements can create copies nobody tracked. Organizations that resolved the cloud-versus-residency conflict properly — by classifying data and writing rules by class — can answer the AI question in weeks. Those that papered over it with a blanket policy and a stack of exceptions are discovering that their staff are already using AI, that the data classification work was never done, and that they are now doing it retrospectively under pressure. The lesson is unglamorous and consistent: policy that has not been reconciled with other policy is not a control. It is a document that will be overridden by the first project with a deadline.
Common Questions
What is a cloud-first policy?
A mandate that new systems should be deployed on cloud infrastructure by default, with on-premise or private hosting requiring specific justification. It is usually adopted to overcome inertia around aging internal infrastructure.
Why do cloud-first policies conflict with data residency rules?
Because cloud providers optimise for global infrastructure while residency rules require data to remain in specified jurisdictions. The conflict surfaces when a preferred provider has no region in the required country.
How should organizations resolve the conflict?
By classifying data and writing residency rules per class rather than blanket, making region availability a vendor screening criterion, and defining a controlled exception process with compensating controls and review dates.
Does storing data in-country satisfy every sovereignty concern?
No. Residency addresses physical location. A foreign-headquartered provider may still be subject to its home jurisdiction's legal process, so legal access risk requires separate assessment.
Cloud Policy Alignment Review — Outpace reconciles your cloud mandate with your residency obligations into one decision matrix, audits the exceptions already granted, and tells you where your regulated data actually sits.